An employee leaves, and nobody is quite sure who controls the advertising account, domain registrar or shared design subscription. A password exists somewhere in a chat history. The recovery phone belongs to a former colleague. These are operational problems before they become security incidents, and they are a good starting point for evaluating a business password manager.
The purchasing decision should focus on access throughout an employee’s time with the company: joining, changing responsibilities and leaving. Convenient sign-in matters, but so do ownership, recovery and the ability to remove access without bringing ordinary work to a halt.
Business password managers: inventory access first
Make a list of important services and their owners. Include email, hosting, domain names, payment systems, advertising platforms, analytics and subscriptions used by contractors. Record whether each service supports individual accounts or relies on a shared login. Where individual access is available, use it instead of making shared credentials the default.
For a marketing agency, separate the agency’s own accounts from client-owned systems. Agree who controls recovery information and what happens when an engagement ends.
What makes a business password manager different?
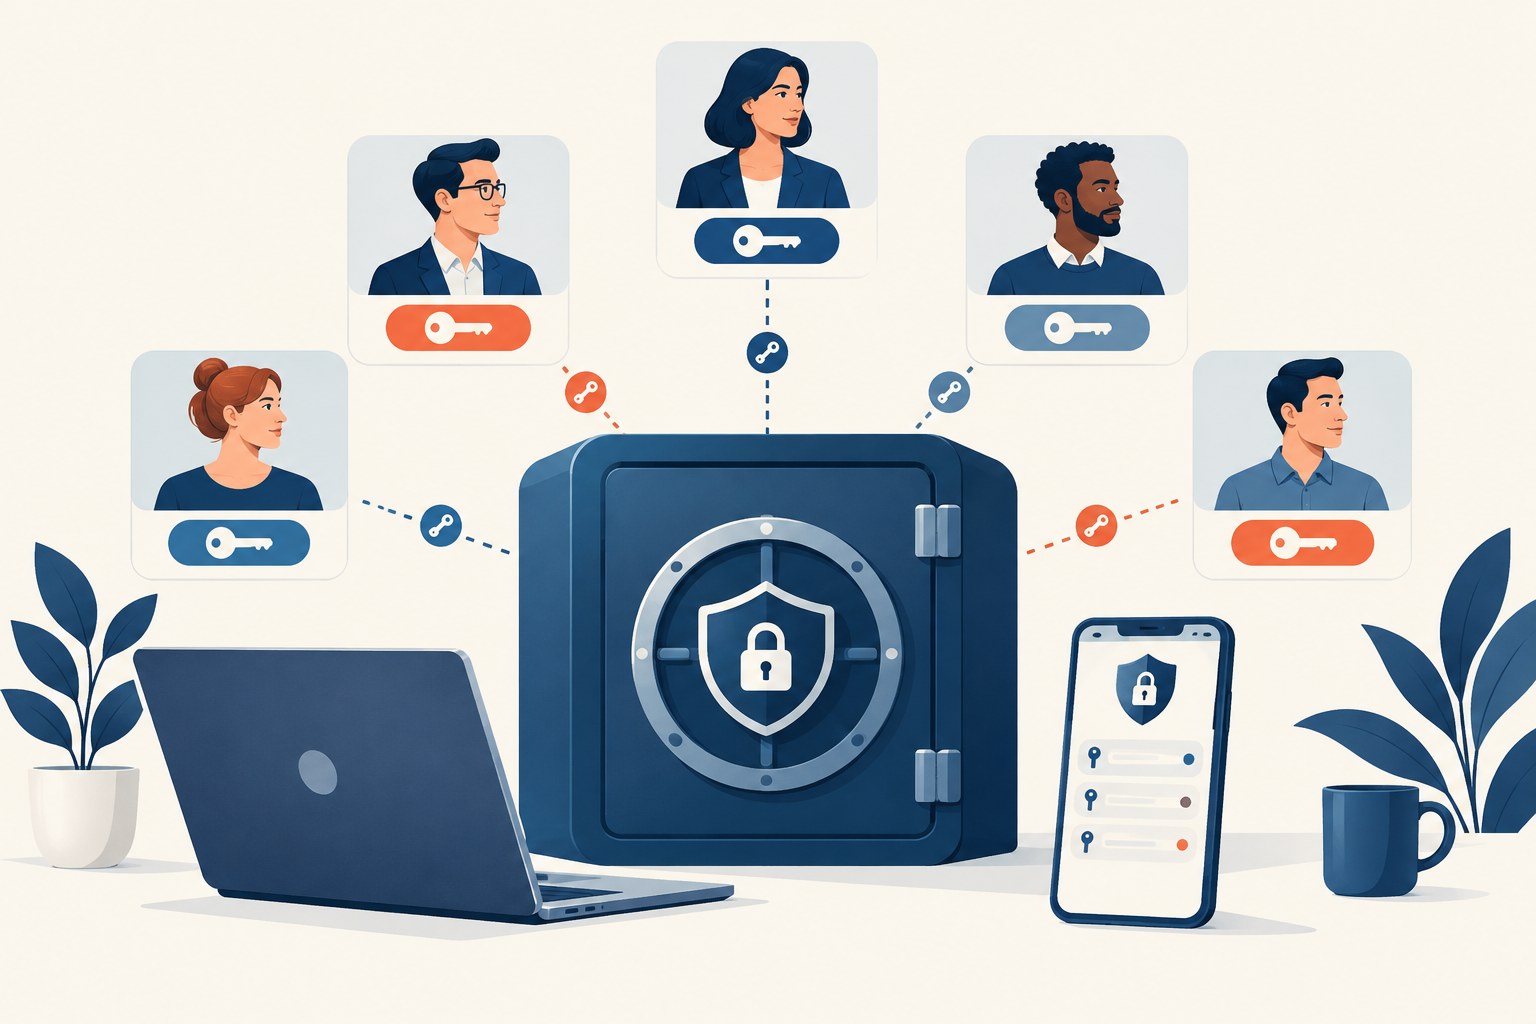
The evaluation goes beyond storing a list of secrets. Look for team administration, appropriate sharing, access policies, activity records and recovery options. Ask how employees are added and removed, how responsibilities are divided and how the organisation handles an unavailable administrator. The exact combination varies by provider and plan.
Bitwarden’s business product page presents password management for organisations rather than only individual users. It offers a starting point for a shortlist, not a substitute for testing your requirements. Request a demonstration with roles resembling your own team, including a manager, an ordinary employee and a temporary external collaborator.
Treat passkeys as part of the decision
Passkeys are increasingly part of the sign-in conversation, so buyers should check how shortlisted products support them across their actual devices and services. 1Password’s documentation explains saving and using passkeys in the browser and notes administrative controls for business accounts. That makes compatibility and management worth testing alongside traditional passwords.
Do not assume every account can move to the same method immediately. Some services will offer different sign-in options or have practical restrictions. Build a short compatibility list using the systems your staff need daily. Check recovery and transfer procedures before making a new authentication method essential to an important business workflow.
Test sharing with a realistic agency scenario
Imagine a designer needs access to one client’s stock-image subscription for two weeks. The account manager needs ongoing access, while another client team should have none. Ask the provider to demonstrate that arrangement, then remove the temporary collaborator. Check what access actually disappears and what action remains necessary in the original service.
Removing an item from someone’s vault does not necessarily invalidate a password they already know or end an existing session elsewhere. Your offboarding process may still require changing credentials and revoking sessions in the connected service. Ask the vendor to explain these boundaries clearly. A password manager is one component of access management, not control over every external system.
Make recovery an ordinary test, not an emergency
Ask what happens when an employee loses a phone or forgets how to unlock their account. Then ask what happens when the administrator is unavailable. Who can approve recovery? What verification is required? Which information can be restored, and which cannot? Have the vendor explain the trade-offs rather than promising that recovery is effortless in every circumstance.
Document the process and test it with noncritical accounts. Keep emergency access arrangements controlled and known to the appropriate owners. At the same time, making recovery too easy can undermine the protection you intended to buy.
Review the evidence behind security claims
Read the provider’s security documentation and look for published information about independent assessments. Check the scope and date of any audit rather than relying on a badge. Ask how incidents are communicated and how administrators can review important activity.
The service also needs to work with the organisation’s wider controls. Review device security, multifactor authentication and staff training with the person responsible for IT. A well-managed vault cannot compensate for every unsafe device or fraudulent request. Make the division of responsibilities clear enough that staff know when to stop and ask for help.
Compare the full subscription cost
Calculate the cost for employees, administrators and external collaborators. Check whether features you consider essential require a higher tier. Ask about minimum seats, annual commitments and changes in headcount. Include the staff time needed for rollout, training and cleaning up old shared accounts.
Use the trial to test export and exit arrangements as well. Confirm which information can be moved and what may need to be recreated at individual services. Store any exported material securely during testing and remove it when no longer needed.
Roll out in manageable stages
Start with a small group and a limited set of accounts. Agree on naming, ownership and sharing rules before inviting everyone. Check that staff can find the correct login and distinguish a client account from an internal one. Expand after the process works, then review access whenever responsibilities change.
Common questions from small teams
Is a browser’s password storage enough?
It may meet an individual’s needs, but a business should assess shared access, administration, recovery and offboarding separately. Choose based on those requirements rather than assuming that storing passwords is the entire job.
Can we stop using individual accounts?
No. Where a service supports named users and suitable permissions, retain them. A password manager should help organise access, not erase accountability by making everyone use one identity.
What should decide the purchase?
Pick the service your team can use correctly and your administrator can manage confidently. Insist on a realistic demonstration of joining, sharing, recovery and leaving.
For brands and agencies
Planning a campaign in this category? Explore advertising on ReviewStreet for sponsored articles, guest contributions and relevant link-insertion enquiries. Send your brief to reviewstreet.in@gmail.com. Commercial placements are subject to editorial review and appropriate disclosure.